


PAM-DEF Exam Study Guide Free Practice Test LAST UPDATED DATE Apr 01, 2024
The New PAM-DEF 2024 Updated Verified Study Guides & Best Courses
NEW QUESTION # 16
PSM captures a record of each command that was executed in Unix.
- A. TRIE
- B. FALSE
Answer: A
Explanation:
Explanation
PSM captures a record of each command that was executed in Unix by using the SSH text recorder. This is a feature that enables PSM to record all the keystrokes that are typed during privileged sessions on SSH connections, including Unix systems. The SSH text recorder can be configured in the Platform Management settings for each platform that uses the SSH protocol. The text recordings are stored and protected in the Vault server and are accessible to authorized auditors. The text recordings can also be used for auditing and compliance purposes, as they provide a detailed trace of the actions performed by the users on the target systems1. References:
* 1: Introduction to PSM for SSH, How it works subsection, Text recordings paragraph
NEW QUESTION # 17
When creating an onboarding rule, it will be executed upon .
- A. All accounts in the pending accounts list
- B. Any future accounts discovered by a discovery process
- C. Both "All accounts in the pending accounts list" and "Any future accounts discovered by a discovery process"
Answer: C
Explanation:
Explanation
According to the CyberArk Defender PAM documentation1, when creating an onboarding rule, it will be executed upon both all accounts in the pending accounts list and any future accounts discovered by a discovery process. This means that the rule will automatically onboard and provision the accounts that match the rule criteria, regardless of when they were discovered. The rule will also apply to any new accounts that are discovered by subsequent discovery processes. This way, the onboarding rule can minimize the time and effort required to securely manage the accounts in the vault.
NEW QUESTION # 18
A new domain controller has been added to your domain. You need to ensure the CyberArk infrastructure can use the new domain controller for authentication.
Which locations must you update?
- A. on the Vault server in Windows\System32\Etc\Hosts and on the PVWA server in Windows\System32\Etc\Hosts
- B. in the Private Ark client under Tools > Administrative Tools > Directory Mapping
- C. on the Vault server in Windows\System32\Etc\Hosts and in the PVWA Application under Administration > LDAP Integration > Directories > Hosts
- D. on the Vault server in the certificate store and on the PVWA server in the certificate store
Answer: B
NEW QUESTION # 19
DRAG DROP
Arrange the steps to restore a Vault using PARestore for a Backup in the correct sequence.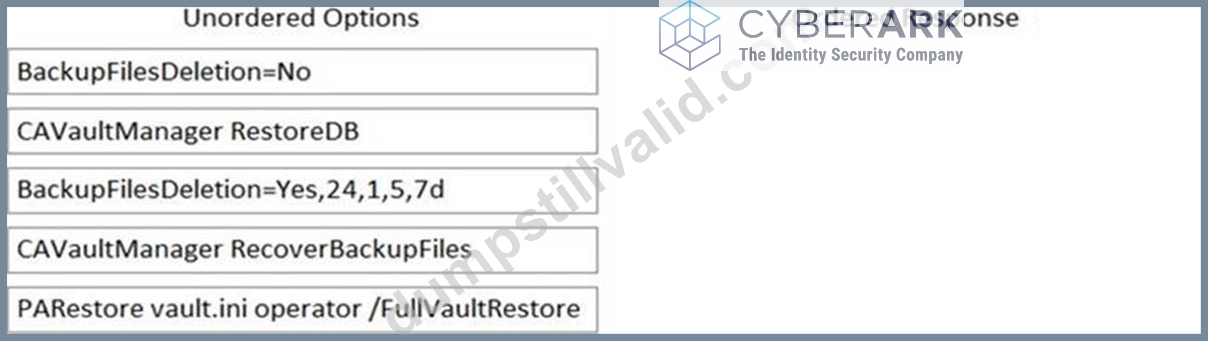
Answer:
Explanation: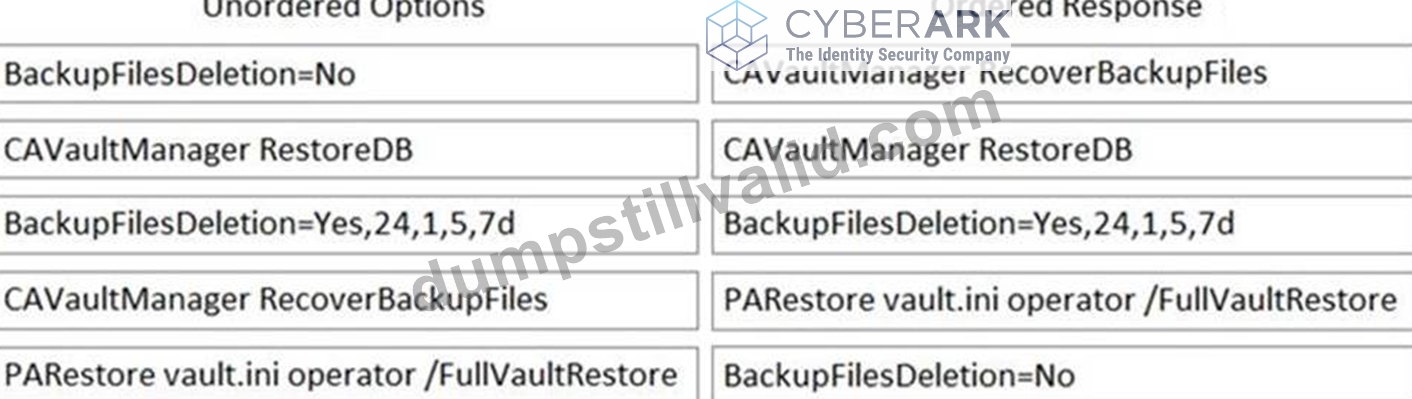
NEW QUESTION # 20
A user has successfully conducted a short PSM session and logged off. However, the user cannot access the Monitoring tab to view the recordings.
What is the issue?
- A. The user is not a member of the Auditors group
- B. The user is not a member of the PVWAMonitor group
- C. The PSM service is not running
- D. The user must login as PSMAdminConnect
Answer: A
NEW QUESTION # 21
In accordance with best practice, SSH access is denied for root accounts on UNIX/LINUX system. What is the BEST way to allow CPM to manage root accounts.
- A. Configure the Unix system to allow SSH logins.
- B. Create a non-privileged account on the target server. Allow this account the ability to SSH directly from the CPM machine. Configure this account as the Logon account of the target server's root account.
- C. Configure the CPM to allow SSH logins.
- D. Create a privileged account on the target server. Allow this account the ability to SSH directly from the CPM machine. Configure this account as the Reconcile account of the target server's root account.
Answer: B
Explanation:
Explanation
https://docs.cyberark.com/Product-Doc/OnlineHelp/PAS/Latest/en/Content/PASIMP/Using-Logon-Accounts-for
NEW QUESTION # 22
How much disk space do you need on the server for a PAReplicate?
- A. 1 TB
- B. same as disk size on Primary Vault
- C. same as disk size on Satellite Vault
- D. 500 GB
Answer: B
NEW QUESTION # 23
Due to corporate storage constraints, you have been asked to disable session monitoring and recording for 500 testing accounts used for your lab environment.
How do you accomplish this?
- A. Master Policy>select Session Management>add Exceptions to the platform(s)>disable Session Monitoring and Recording policies
- B. Administration>Platform Management>select the platform(s)>disable Session Monitoring and Recording Most Voted
- C. Polices>Access Control (Safes)>select the safe(s)>disable Session Monitoring and Recording policies
- D. Administration>Configuration Options>Options>select Privilege Session Management>disable Session Monitoring and Recording policies
Answer: D
Explanation:
Explanation
To disable session monitoring and recording for a large number of accounts due to storage constraints, you would navigate to the Administration section of the CyberArk Privileged Access Security (PAS) solution, specifically to the Configuration Options. From there, you would select the Privilege Session Management (PSM) options and disable the Session Monitoring and Recording policies. This action would apply the changes to the specified accounts, thus disabling the session monitoring and recording features for them1.
References: The answer is based on general knowledge of CyberArk PAS and best practices for managing session policies within the system. For specific steps and detailed procedures, please refer to the official CyberArk Defender PAM course materials and documentation
NEW QUESTION # 24
If the AccountUploader Utility is used to create accounts with SSH keys, which parameter do you use to set the full or relative path of the SSH private key file that will be attached to the account?
- A. KeyPath
- B. KeyFile
- C. ObjectName
- D. Address
Answer: B
NEW QUESTION # 25
Can the 'Connect' button be used to initiate an SSH connection, as root, to a Unix system when SSH access for root is denied?
- A. No, it is not possible.
- B. Yes, only if a logon account is associated with the root account and the user connects through the PSM-SSH connection component.
- C. Yes, when using the connect button, CyberArk uses the PMTerminal.exe process which bypasses the root SSH restriction.
- D. Yes, if a logon account is associated with the root account.
Answer: B
Explanation:
Explanation
The 'Connect' button is a feature of the PVWA that allows users to initiate a privileged session to a target system through PSM without revealing the account credentials. The 'Connect' button can be used to initiate an SSH connection, as root, to a Unix system when SSH access for root is denied, but only if a logon account is associated with the root account and the user connects through the PSM-SSH connection component. A logon account is a linked account that contains the password required to log on to a remote machine in order to perform a task using the regular account. A common use case for using a logon account is managing root accounts on a Unix system. The best practice for Unix systems is to disallow the root user from logging in using SSH. However, SSH is what the PSM uses to sign in to a system to manage the password. To manage the root password without violating this practice, the PSM establishes the session with a non-root account and then SUs to root (the target account). This is done using a linked account called a logon account. The PSM-SSH connection component is a predefined connection component that enables users to connect to Unix systems through PSM using SSH. The PSM-SSH connection component supports the use of logon accounts to access root accounts on Unix systems1.
The other options are not correct, because:
* A. Yes, when using the connect button, CyberArk uses the PMTerminal.exe process which bypasses the root SSH restriction. This is not correct, because PMTerminal.exe is a process that is used by the PSM-RDP connection component, not the PSM-SSH connection component. PMTerminal.exe is a terminal emulator that enables users to connect to Windows systems through PSM using RDP. PMTerminal.exe does not bypass the root SSH restriction, but rather uses the credentials stored in the Vault to authenticate to the target system2.
* C. Yes, if a logon account is associated with the root account. This is not correct, because a logon account alone is not sufficient to initiate an SSH connection, as root, to a Unix system when SSH access for root is denied. The user also needs to connect through the PSM-SSH connection component, which supports the use of logon accounts to access root accounts on Unix systems1.
* D. No, it is not possible. This is not correct, because it is possible to initiate an SSH connection, as root, to a Unix system when SSH access for root is denied, as explained in option B.
References:
* 1: Logon Accounts for SSH and Telnet Connections
* 2: Connect through PSM for SSH
NEW QUESTION # 26
When managing SSH keys, the CPM stored the Private Key
- A. On the target server
- B. In the Vault
- C. A & B
- D. Nowhere because the private key can always be generated from the public key.
Answer: B
NEW QUESTION # 27
It is possible to restrict the time of day, or day of week that a [b]reconcile[/b] process can occur
- A. FALS
- B. TRUE
Answer: B
NEW QUESTION # 28
Which methods can you use to add a user directly to the Vault Admin Group? (Choose three.)
- A. Active Directory
- B. PACLI
- C. Sailpoint
- D. PVWA
- E. PrivateArk Client
- F. REST API
Answer: B,E,F
Explanation:
Explanation
To add a user directly to the Vault Admin Group in CyberArk, you can use the following methods:
* REST API: The REST API allows for programmatic management of users and groups within the Vault, including adding users to the Vault Admin Group1.
* PrivateArk Client: The PrivateArk Client provides a graphical interface for managing users and groups, and it can be used to add users directly to the Vault Admin Group2.
* PACLI: The PACLI (Privileged Access Command Line Interface) is a command-line tool that enables administrators to manage the Vault, including adding users to groups2.
These methods provide different ways to manage users and their group memberships within the CyberArk Vault, offering flexibility for administrators to choose the most suitable approach for their needs.
References:
* CyberArk's official documentation on using the REST API to manage users and groups1.
* Information on managing users and groups through the PrivateArk Client and PACLI2.
NEW QUESTION # 29
You created a new platform by duplicating the out-of-box Linux through the SSH platform.
Without any change, which Text Recorder Type(s) will the new platform support? (Choose two.)
- A. SSH Text Recorder
- B. Telnet Commands Text Recorder
- C. SQL Text Recorder
- D. Universal Keystrokes Text Recorder
- E. Events Text Recorder
Answer: A,D
NEW QUESTION # 30
A Logon Account can be specified in the Master Policy.
- A. FALSE
- B. TRUE
Answer: A
NEW QUESTION # 31
To use PSM connections while in the PVWA, what are the minimum safe permissions a user or group will need?
- A. Use Accounts
- B. List Accounts, Use Accounts, Retrieve Accounts, Access Safe without confirmation
- C. List Accounts, Use Accounts, Retrieve Accounts
- D. List Accounts, Use Accounts
Answer: C
Explanation:
Explanation
To use PSM connections within the PVWA, a user or group needs to have permissions that allow them to list and use accounts, as well as retrieve account details. These permissions ensure that the user can view the accounts within a safe, initiate sessions using those accounts, and retrieve the necessary credentials for authentication during the session initiation process1.
References:
* CyberArk's official documentation on Safe Settings and permissions required for each safe in CyberArk's Enterprise Password Vault (EPV) components provides detailed information on the default safe configuration and permissions1.
* For more information on best practices for safe and safe member design, including the minimum permissions required for PSM connections, refer to CyberArk's best practices articles and study guides
NEW QUESTION # 32
It is possible to restrict the time of day, or day of week that a [b]verify[/b] process can occur
- A. FALSE
- B. TRUE
Answer: B
Explanation:
Explanation
Password verification can be restricted to specific days. This means that the CPM will only verify passwords on the days of the week specified in the VFExecutionDays parameter. The days of the week are represented by the first 3 letters of the name of the day. Sunday is represented by Sun, Monday by Mon, etc.
NEW QUESTION # 33
If a user is a member of more than one group that has authorizations on a safe, by default that user is granted________.
- A. the cumulative permissions of all groups to which that user belongs.
- B. the vault will not allow this situation to occur.
- C. only those permissions that exist on the group added to the safe first.
- D. only those permissions that exist in all groups to which the user belongs.
Answer: C
NEW QUESTION # 34
You have been asked to secure a set of shared accounts in CyberArk whose passwords will need to be used by end users. The account owner wants to be able to track who was using an account at any given moment.
Which security configuration should you recommend?
- A. Configure shared account mode on the appropriate safe.
- B. Configure both one-time passwords and exclusive access for the appropriate platform in Master Policy.
- C. Configure object level access control on the appropriate safe.
- D. Configure one-time passwords for the appropriate platform in Master Policy.
Answer: C
NEW QUESTION # 35
......
Get Prepared for Your PAM-DEF Exam With Actual 240 Questions: https://www.dumpstillvalid.com/PAM-DEF-prep4sure-review.html
Authentic PAM-DEF Exam Dumps PDF - 2024 Updated: https://drive.google.com/open?id=1F5HaWfHWrbyr8N6jL5HrVWx9AF38gM4E
