


(Nov-2025) Get professional help from our PAM-DEF Dumps PDF
Give You Free Regular Updates on PAM-DEF Exam Questions
CyberArk PAM-DEF exam is a certification that validates the knowledge and skills of professionals in the field of Privileged Access Management (PAM). CyberArk Defender - PAM is a comprehensive solution that helps organizations protect their critical assets and sensitive information from cyber threats. CyberArk Defender - PAM certification exam is designed to test the knowledge of candidates in the areas of PAM architecture, installation, configuration, and management.
The CyberArk PAM-DEF exam consists of multiple-choice questions and is administered online. PAM-DEF exam is timed and candidates must complete it within the allotted time. PAM-DEF exam questions are designed to test the candidate's knowledge of CyberArk's Privileged Access Security solution and their ability to apply that knowledge in real-world scenarios.
NEW QUESTION # 109
In PVWA, you are attempting to play a recording made of a session by user jsmith, but there is no option to "Fast Forward" within the video. It plays and only allows you to skip between commands instead. You are also unable to download the video.
What could be the cause?
- A. Recording is of a PSM for SSH session.
- B. The browser you are using is out of date and needs an update to be supported.
- C. You do not have the "View Audit" permission on the safe where the account is stored.
- D. You need to update the recorder settings in the platform to enable screen capture every 10000 ms or less.
Answer: B
NEW QUESTION # 110
Which PTA sensors are required to detect suspected credential theft?
- A. Logs, Vault Logs
- B. Logs, Network Sensor, EPM
- C. Logs, Network Sensor, Vault Logs
- D. Logs, PSM Logs, CPM Logs
Answer: A
NEW QUESTION # 111
Users are unable to launch Web Type Connection components from the PSM server. Your manager asked you to open the case with CyberArk Support.
Which logs will help the CyberArk Support Team debug the issue? (Choose three.)
- A. <Session_ID>.Component.log
- B. ITAlog.log
- C. PMconsole.log
- D. PSMTrace.log
- E. PSMConsole.log
- F. PSMDebug.log
Answer: A,D,E
Explanation:
Explanation
When users are unable to launch Web Type Connection components from the PSM server, the CyberArk Support Team will require specific logs to debug the issue. The logs that are typically helpful in such cases include:
* PSMConsole.log: This log file contains informational messages and errors related to the PSM function, which can help identify issues with the PSM server's operation1.
* PSMTrace.log: This log file includes errors and trace messages, which can provide detailed insights into the issues occurring during the PSM server's processes1.
* <Session_ID>.Component.log: This log file contains errors and trace messages related to the connection component, which can be crucial for troubleshooting issues with launching Web Type Connection components1.
These logs can provide the necessary information to understand the problem and assist the support team in resolving the issue effectively.
References:
* CyberArk's official documentation on PSM for Web Troubleshooting, which outlines the types of logs available and their purposes in the troubleshooting process1.
* Additional resources on managing and interpreting PSM logs, which provide guidance on using logs for diagnosing and resolving issues with the PSM server2
NEW QUESTION # 112
Which Cyber Are components or products can be used to discover Windows Services or Scheduled Tasks that use privileged accounts? Select all that apply.
- A. Accounts Discovery
- B. Auto Detection (AD)
- C. On Demand Privileges Manager (OPM)
- D. Discovery and Audit (DMA)
- E. Export Vault Data (EVD)
Answer: A,B,D
Explanation:
Explanation
Discovery and Audit (DMA), Auto Detection (AD), and Accounts Discovery are CyberArk components or products that can be used to discover Windows Services or Scheduled Tasks that use privileged accounts.
* Discovery and Audit (DMA) is a tool that scans Windows servers and workstations to identify privileged accounts that are used by Windows Services or Scheduled Tasks. DMA can also generate reports on the usage and risks of these accounts.
* Auto Detection (AD) is a feature of the CyberArk Privileged Account Security Solution that automatically detects and onboards privileged accounts that are used by Windows Services or Scheduled Tasks. AD can also monitor and rotate the passwords of these accounts.
* Accounts Discovery is a feature of the CyberArk Privileged Account Security Solution that scans the network to discover privileged accounts on various platforms, including Windows. Accounts Discovery can also identify accounts that are used by Windows Services or Scheduled Tasks.
References:
* : Discovery and Audit (DMA) User Guide
* : Auto Detection Implementation Guide
* : Accounts Discovery Implementation Guide
NEW QUESTION # 113
In a default CyberArk installation, which group must a user be a member of to view the "reports" page in PVWA?
- A. ReportUsers
- B. PVWAMonitor
- C. PVWAReports
- D. Operators
Answer: B
NEW QUESTION # 114
What is the purpose of the HeadStartlnterval setting m a platform?
- A. It determines how far in advance audit data is collected tor reports
- B. It instructs the CPM to initiate the password change process X number of days before expiration.
- C. It alerts users of upcoming password changes x number of days before expiration.
- D. It instructs the AIM Provider to 'skip the cache' during the defined time period
Answer: B
Explanation:
Explanation
The purpose of the HeadStartInterval setting in a platform is to instruct the CPM to initiate the password change process X number of days before expiration. This setting is used when the platform has the One Time Password feature enabled, which means that the passwords are changed every time they are retrieved by a user. The HeadStartInterval setting defines the number of days before the password expires (according to the ExpirationPeriod parameter) that the CPM will start the password change process. This gives the CPM enough time to change the password before it becomes invalid, and ensures that the user will always receive a valid password when they request it1. The HeadStartInterval setting can be configured in the Platform Management settings for each platform that supports One Time Passwords. The default value is 0, which means that the CPM will start the password change process on the same day as the password expiration date1.
The other options are not the purpose of the HeadStartInterval setting in a platform:
* A. It determines how far in advance audit data is collected for reports. This option is not related to the HeadStartInterval setting, which does not affect the audit data collection or reporting. The audit data is collected by the Vault server and stored in the Audit database, and the reports are generated by the PVWA or the PrivateArk Client based on the audit data2.
* C. It instructs the AIM Provider to 'skip the cache' during the defined time period. This option is not related to the HeadStartInterval setting, which does not affect the AIM Provider or the cache mechanism. The AIM Provider is a component that enables applications to securely retrieve credentials from the Vault without requiring human intervention. The cache mechanism is a feature that allows the AIM Provider to store credentials locally for a limited time, in case of a temporary network failure or Vault unavailability3.
* D. It alerts users of upcoming password changes x number of days before expiration. This option is not related to the HeadStartInterval setting, which does not alert users of anything. The HeadStartInterval setting only instructs the CPM to initiate the password change process, not to notify the users. The users
* do not need to be aware of the password changes, as they are performed automatically by the CPM and do not affect the user experience1. References:
* 1: Privileged Account Management, Min Validity Period subsection
* 2: Reports and Audits
* 3: Application Identity Manager
NEW QUESTION # 115
Which onboarding method would you use to integrate CyberArk with your accounts provisioning process?
- A. Onboarding RestAPI functions
- B. Accounts Discovery
- C. PTA Rules
- D. Auto Detection
Answer: A
Explanation:
Explanation
The Onboarding RestAPI functions are a set of web services that allow you to integrate CyberArk with your accounts provisioning process. You can use the Onboarding RestAPI functions to create, update, delete, or verify accounts in the CyberArk Vault, as well as to retrieve information about accounts, platforms, and safes.
The Onboarding RestAPI functions are part of the Central Credential Provider component, which is installed on a dedicated server that communicates with the Vault. References:
* [Defender PAM Course], Module 4: Onboarding Accounts, Lesson: Onboarding RestAPI Functions
* [Onboarding RestAPI Functions Guide], Introduction
NEW QUESTION # 116
Due to corporate storage constraints, you have been asked to disable session monitoring and recording for 500 testing accounts used for your lab environment.
How do you accomplish this?
- A. Administration>Platform Management>select the platform(s)>disable Session Monitoring and Recording Most Voted
- B. Master Policy>select Session Management>add Exceptions to the platform(s)>disable Session Monitoring and Recording policies
- C. Administration>Configuration Options>Options>select Privilege Session Management>disable Session Monitoring and Recording policies
- D. Polices>Access Control (Safes)>select the safe(s)>disable Session Monitoring and Recording policies
Answer: A
NEW QUESTION # 117
Which CyberArk utility allows you to create lists of Master Policy Settings, owners and safes for output to text files or MSSQL databases?
- A. Privileged Threat Analytics
- B. Export Vault Information
- C. PrivateArk Client
- D. Export Vault Data
Answer: B
Explanation:
Explanation
The Export Vault Information utility is a CyberArk tool that allows you to create lists of Master Policy settings, owners and safes for output to text files or MSSQL databases. This utility can be used to export various types of information from the Vault, such as accounts, safes, platforms, policies, users, groups, and audit records. The utility can also generate reports based on predefined templates or custom queries. The utility can be run from the command line or the graphical user interface. References: Export Vault Information, Export Vault Information Utility
NEW QUESTION # 118
In the Private Ark client, how do you add an LDAP group to a CyberArk group?
- A. Select Update on the CyberArk group, and then click Add > LDAP Group
- B. Select Update on the LDAP Group, and then click Add > LDAP Group
- C. Select Member Of on the CyberArk group, and then click Add > LDAP Group
- D. Select Member Of on the LDAP group, and then click Add > LDAP Group
Answer: B
NEW QUESTION # 119
Which report provides a list of account stored in the vault.
- A. Privileged Accounts Compliance Status
- B. Entitlement Report
- C. Privileged Accounts Inventory
- D. Active Log
Answer: C
Explanation:
Explanation
The report that provides a list of accounts stored in the vault is the Privileged Accounts Inventory report. This report can be generated in the Reports page in the PVWA by users who belong to the group that is specified in the ManageReportsGroup parameter in the Reports section of the Web Access Options in the System Configuration page1. The Privileged Accounts Inventory report contains information such as the safe, folder, name, platform ID, username, address, group, last accessed date, last accessed by, last modified date, last modified by, verification date, checkout date, checked out by, age, change failure, verification failure, master pass folder, master pass name, disabled by, and disabled reason of each account stored in the vault2.
References:
* 1: Reports in PVWA
* 2: Users List Report
NEW QUESTION # 120
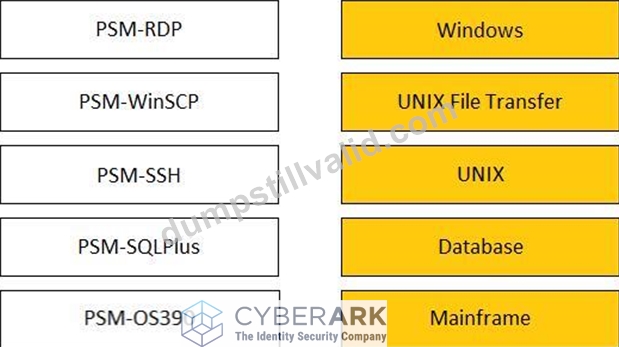
Match the connection component to the corresponding OS/Function.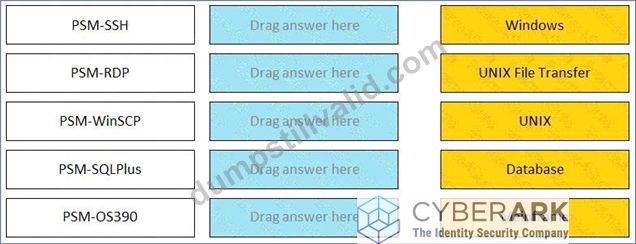
Answer:
Explanation: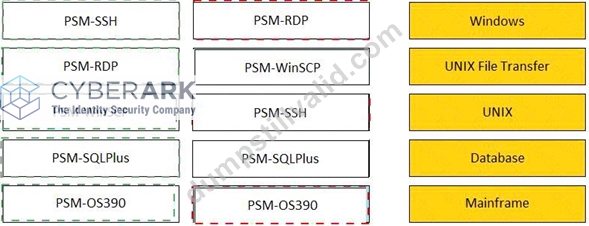
NEW QUESTION # 121
What is the easiest way to duplicate an existing platform?
- A. From PrivateArk, copy/paste the appropriate settings in PVConfiguration.xml; then update the policyName variable.
- B. From the PVWA, navigate to the platforms page, select an existing platform that is similar to the new target account platform, manually update the platform settings and click "Save as" INSTEAD of save to duplicate and rename the platform.
- C. From PrivateArk, copy/paste the appropriate Policy.ini file; then rename it.
- D. From the PVWA, navigate to the platforms page, select an existing platform that is similar to the new target account platform and then click Duplicate; name the new platform.
Answer: D
Explanation:
Explanation
The easiest way to duplicate an existing platform is to use the PVWA, which is the web interface that allows users to access and manage the CyberArk Defender PAM system. The PVWA has a platforms page that displays all the platforms that are available in the system, categorized by platform types. Users can duplicate an existing platform by selecting it, clicking the ellipsis button next to it, and then clicking Duplicate. This will create a copy of the platform with the same settings and properties, which can be customized according to the user's needs. Users can name the new platform and save it in the system. References: Manage platforms - CyberArk
NEW QUESTION # 122
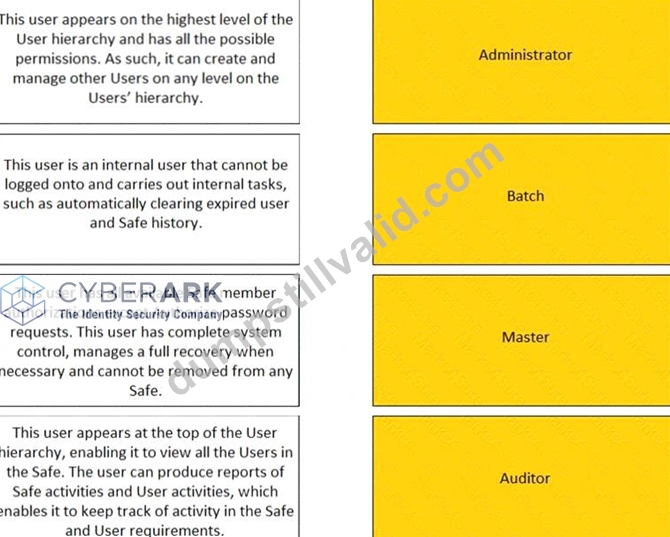
Match the built-in Vault User with the correct definition.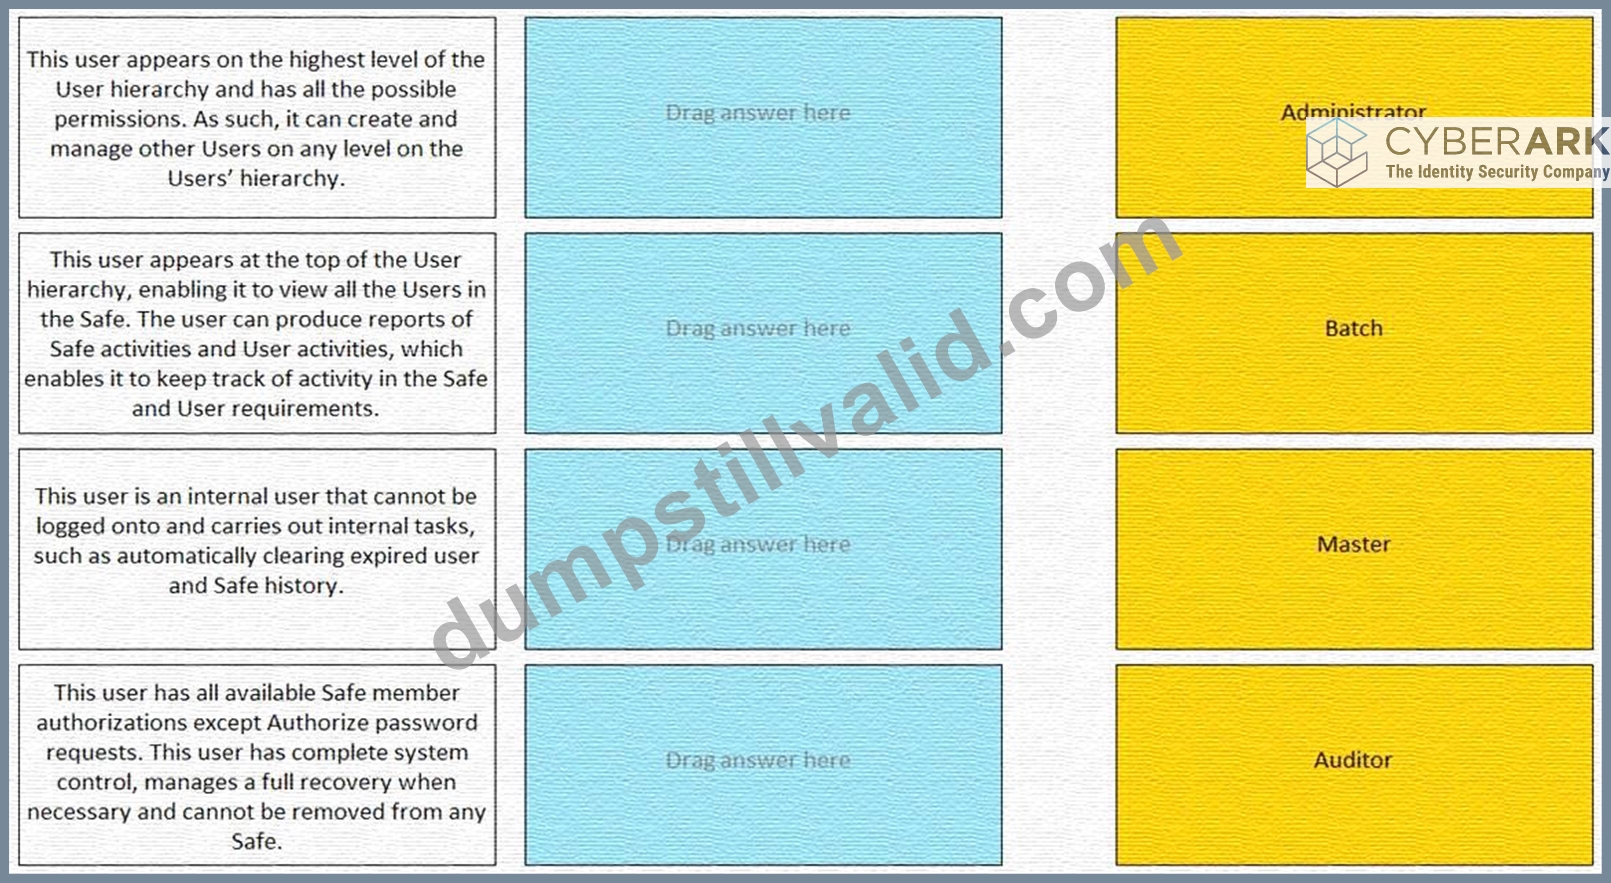
Answer:
Explanation: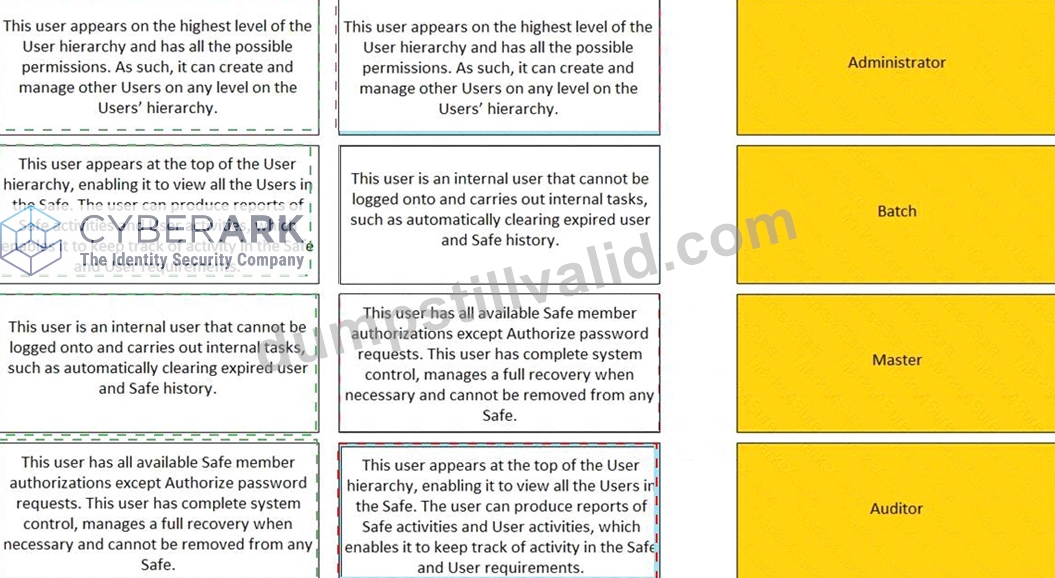
NEW QUESTION # 123
Match the connection component to the corresponding OS/Function.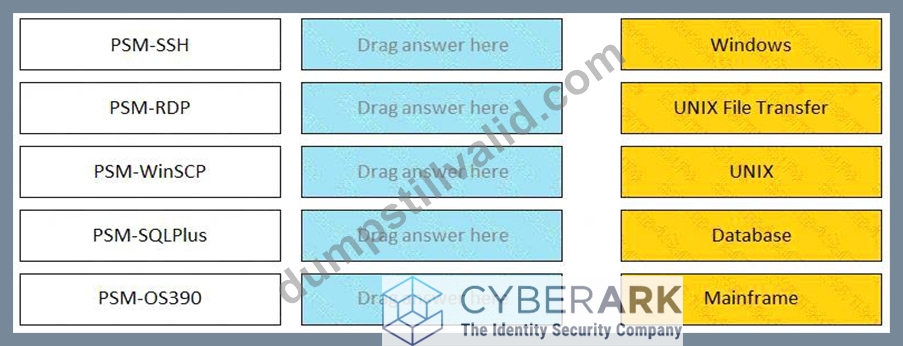
Answer:
Explanation: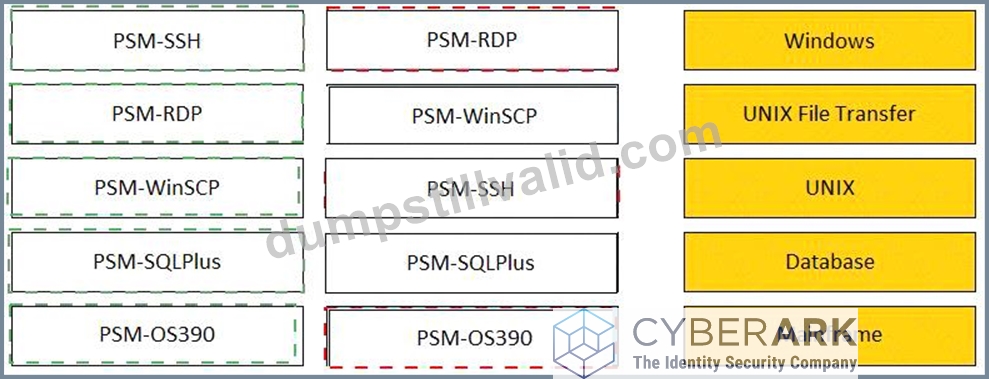
NEW QUESTION # 124
In the Private Ark client, how do you add an LDAP group to a CyberArk group?
- A. Select Member Of on the LDAP group, and then click Add > LDAP Group
- B. Select Update on the CyberArk group, and then click Add > LDAP Group
- C. Select Member Of on the CyberArk group, and then click Add > LDAP Group
- D. Select Update on the LDAP Group, and then click Add > LDAP Group
Answer: A
NEW QUESTION # 125
Which of the following statements are NOT true when enabling PSM recording for a target Windows server? (Choose all that apply)
- A. PSM must be enabled in the Master Policy (either directly, or through exception)
- B. The PSM software must be instated on the target server
- C. RDP must be enabled on the target server
- D. PSMConnect must be added as a local user on the target server
Answer: A,B
NEW QUESTION # 126
Which dependent accounts does the CPM support out-of-the-box? (Choose three.)
- A. Windows DCOM Applications
- B. Windows Services
- C. Solaris Configuration file
- D. Key Tab file
- E. Windows Scheduled
- F. Windows Registry
Answer: B,E,F
NEW QUESTION # 127
......
CyberArk PAM-DEF exam is a comprehensive test that covers a wide range of topics related to PAM. PAM-DEF exam assesses a candidate’s knowledge of CyberArk solutions, including the installation and configuration of CyberArk components, the management of privileged accounts, and the creation of policies and workflows. PAM-DEF exam also covers advanced topics such as integration with other security solutions, automation, and reporting.
Achieve the PAM-DEF Exam Best Results with Help from CyberArk Certified Experts: https://www.dumpstillvalid.com/PAM-DEF-prep4sure-review.html
Provide PAM-DEF Practice Test Engine for Preparation: https://drive.google.com/open?id=1F5HaWfHWrbyr8N6jL5HrVWx9AF38gM4E
