


Get CS0-001 Actual Free Exam Q&As to Prepare for Your CompTIA Certification
CompTIA Actual Free Exam Questions And Answers
The CySA+ certification exam is ideal for IT professionals who want to advance their careers in cybersecurity. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification is suitable for individuals who have experience in the field of IT and want to specialize in cybersecurity. It is also a great option for those who are looking to transition into cybersecurity from other IT roles, such as network administration or system administration.
CompTIA CySA+ certification is an excellent certification for IT professionals who want to advance their careers in the cybersecurity field. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification validates the skills and knowledge required for a cybersecurity analyst role and is recognized by industry leaders and government agencies. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification exam covers essential topics such as threat and vulnerability management, incident response, security operations and monitoring, and compliance and assessment. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification can help IT professionals stand out in the job market and increase their earning potential.
CompTIA CySA+ certification exam covers a wide range of topics related to the cybersecurity domain, including threat management, vulnerability management, incident response, compliance and governance, and security architecture and toolsets. CS0-001 exam is designed for professionals who have at least 3-4 years of hands-on experience in cybersecurity or related fields. Additionally, candidates should have a strong understanding of networking, operating systems, and virtualization technologies.
NEW QUESTION # 42
During a web application vulnerability scan, it was discovered that the application would display
inappropriate data after certain key phrases were entered into a webform connected to a SQL database
server. Which of the following should be used to reduce the likelihood of this type of attack returning
sensitive data?
- A. Static code analysis
- B. Input validation
- C. Application fuzzing
- D. Peer review code
Answer: B
NEW QUESTION # 43
As part of an upcoming engagement for a client, an analyst is configuring a penetration testing application to ensure the scan complies with information defined in the SOW. Which of the following types of information should be considered based on information traditionally found in the SOW? (Select two.)
- A. Timing of the scan
- B. IPS configuration
- C. Maintenance windows
- D. Incident response policies
- E. Excluded hosts
- F. Contents of the executive summary report
Answer: A,E
NEW QUESTION # 44
A security analyst is conducting a vulnerability assessment of older SCADA devices on the corporate network. Which of the following compensating controls is likely to prevent the scans from providing value?
- A. Implementation of a VLAN that allows all devices on the network to see all SCADA devices on the network.
- B. Detailed and tested firewall rules that effectively prevent outside access of the SCADA devices.
- C. SCADA systems configured with 'SCADA SUPPORT'=ENABLE
- D. Access control list network segmentation that prevents access to the SCADA devices inside the network.
Answer: B
NEW QUESTION # 45
During a review of security controls, an analyst was able to connect to an external, unsecured FTP server from a workstation. The analyst was troubleshooting and reviewed the ACLs of the segment firewall the workstation is connected to:
Based on the ACLs above, which of the following explains why the analyst was able to connect to the FTP server?
- A. FTP was allowed in Seq 10 of the ACL.
- B. FTP was explicitly allowed in Seq 8 of the ACL.
- C. FTP was allowed as being outbound from Seq 9 of the ACL.
- D. FTP was allowed as being included in Seq 3 and Seq 4 of the ACL.
Answer: B
NEW QUESTION # 46
A cybersecurity analyst was asked to discover the hardware address of 30 networked assets. From a command line, which of the following tools would be used to provide ARP scanning and reflects the MOST efficient method for accomplishing the task?
- A. tracert
- B. nmap
- C. ping -a
- D. nslookup
Answer: B
Explanation:
Reference https://serverfault.com/questions/10590/how-to-get-a-list-of-all-ip-addresses- and-ideally-device-names-on-a-lan
NEW QUESTION # 47
Following a recent security breach, a post-mortem was done to analyze the driving factors behind the breach. The cybersecurity analysis discussed potential impacts, mitigations, and remediations based on current events and emerging threat vectors tailored to specific stakeholders. Which of the following is this considered to be?
- A. Threat information
- B. Threat intelligence
- C. Advanced persistent threats
- D. Threat data
Answer: B
Explanation:
Section: (none)
NEW QUESTION # 48
A security analyst is running a routine vulnerability scan against a web farm. The farm consists of a single server acting as a load-balancing reverse proxy and offloads cryptographic processes to the backend servers. The backend servers consist of four servers that process the inquiries for the front end.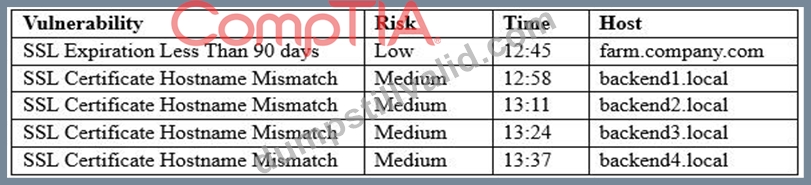
A web service SSL query of each server responds with the same output:
Connected (0x000003)
depth=0 /0=farm.company.com/CN=farm.company.com/OU=Domain Control Validated Which of the following results BEST addresses these findings?
- A. Create an exception in the vulnerability scanner, as the results and false positives and can be ignored safely
- B. Advise the application development team that the SSL certificates on the backend servers should be revoked and reissued to match their hostnames
- C. Require that the application development team renews the farm certificate and includes a wildcard for the 'local' domain in the certificate SAN field
- D. Notify the application development team of the findings and advise management of the results
Answer: A
NEW QUESTION # 49
A security analyst is reviewing a report from the networking department that describes an increase in network utilization, which is causing network performance issues on some systems. A top talkers report over a five-minute sample is included.
Given the above output of the sample, which of the following should the security analyst accomplish FIRST to help track down the performance issues?
- A. Recommend that networking block the unneeded protocols such as Quicktime to clear up some of the congestion.
- B. Quarantine the top talker on the network and begin to investigate any potential threats caused by the excessive traffic.
- C. Put ACLs in place to restrict traffic destined for random or non-default application ports.
- D. Perform reverse lookups on each of the IP addresses listed to help determine if the traffic is necessary.
Answer: D
NEW QUESTION # 50
A cybersecurity analyst was asked to discover the hardware address of 30 networked assets.
From a command line, which of the following tools would be used to provide ARP scanning and reflects the MOST efficient method for accomplishing the task?
- A. tracert
- B. nmap
- C. ping -a
- D. nslookup
Answer: B
Explanation:
Reference https://serverfault.com/questions/10590/how-to-get-a-list-of-all-ip-addresses-and-ideally-device-names-on-a-lan
NEW QUESTION # 51
A technician at a company's retail store notifies an analyst that disk space is being consumed at a rapid rate on several registers. The uplink back to the corporate office is also saturated frequently. The retail location has no Internet access. An analyst then observes several occasional IPS alerts indicating a server at corporate has been communicating with an address on a watchlist. Netflow data shows large quantities of data transferred at those times.
Which of the following is MOST likely causing the issue?
- A. A credit card processing file was declined by the card processor and caused transaction logs on the registers to accumulate longer than usual.
- B. A penetration test is being run against the registers from the IP address indicated on the watchlist, generating large amounts of traffic and data storage.
- C. Ransomware on the corporate network has propagated from the corporate network to the registers and has begun encrypting files there.
- D. Malware on a register is scraping credit card data and staging it on a server at the corporate office before uploading it to an attacker-controlled command and control server.
Answer: D
NEW QUESTION # 52
The new Chief Technology Officer (CTO) is seeking recommendations for network monitoring services for the local intranet. The CTO would like the capability to monitor all traffic to and from the gateway, as well as the capability to block certain content. Which of the following recommendations would meet the needs of the organization?
- A. Recommend installation of an IPS on both the internal and external interfaces of the gateway router.
- B. Recommend installation of an IDS on the internal interface and a firewall on the external interface of the gateway router.
- C. Recommend installation of a firewall on the internal interface and a NIDS on the external interface of the gateway router.
- D. Recommend setup of IP filtering on both the internal and external interfaces of the gateway router.
Answer: C
Explanation:
Explanation/Reference:
Explanation:
NEW QUESTION # 53
A security analyst received a compromised workstation. The workstation's hard drive may contain evidence of criminal activities. Which of the following is the FIRST thing the analyst must do to ensure the integrity of the hard drive while performing the analysis?
- A. Make a copy of the hard drive.
- B. Install it on a different machine and explore the content.
- C. Use write blockers.
- D. Run rm -Rcommand to create a hash.
Answer: C
Explanation:
Explanation/Reference:
NEW QUESTION # 54
A security engineer has been asked to reduce the attack surface on an organization's production environment.
To limit access, direct VPN access to all systems must be terminated, and users must utilize multifactor authentication to access a constrained VPN connection and then pivot to other production systems form a bastion host. The MOST appropriate way to implement the stated requirement is through the use of a:
- A. sinkhole.
- B. jump box
- C. multitenant platform.
- D. single-tenant platform.
Answer: B
NEW QUESTION # 55
Given the following log snippet:
Which of the following describes the events that have occurred?
- A. An attempt to make an SSH connection from an unknown IP address was done using a password.
- B. An attempt to make an SSH connection from outside the network was done using PKI.
- C. An attempt to make an SSH connection from 192.168.1.166 was done using PKI.
- D. An attempt to make an SSH connection from "superman" was done using a password.
Answer: C
NEW QUESTION # 56
A security team is implementing a new vulnerability management program in an environment that has a historically poor security posture. The team is aware of issues patch management in the environment and expects a large number of findings. Which of the following would be the MOST efficient way to increase the security posture of the organization in the shortest amount of time?
- A. Create an SLA stating that remediation actions must occur within 30 days of discovery for all levels of vulnerabilities.
- B. Incorporate prioritization levels into the remediation process and address critical findings first.
- C. Create classification criteria for data residing on different servers and provide remediation only for servers housing sensitive data.
- D. Implement a change control policy that allows the security team to quickly deploy patches in the production environment to reduce the risk of any vulnerabilities found.
Answer: B
NEW QUESTION # 57
Which of the following items represents a document that includes detailed information on when an incident
was detected, how impactful the incident was, and how it was remediated, in addition to incident response
effectiveness and any identified gaps needing improvement?
- A. Chain of custody report
- B. Trends analysis report
- C. Forensic analysis report
- D. Lessons learned report
Answer: D
Explanation:
Explanation/Reference:
Explanation:
NEW QUESTION # 58
A security analyst is running a routine vulnerability scan against a web farm. The farm consists of a single server acting as a load-balancing reverse proxy and offloads cryptographic processes to the backend servers.
The backend servers consist of four servers that process the inquiries for the front end.
A web service SSL query of each server responds with the same output:
Connected (0x000003)
depth=0 /0=farm.company.com/CN=farm.company.com/OU=Domain Control Validated Which of the following results BEST addresses these findings?
- A. Create an exception in the vulnerability scanner, as the results and false positives and can be ignored safely
- B. Advise the application development team that the SSL certificates on the backend servers should be revoked and reissued to match their hostnames
- C. Notify the application development team of the findings and advise management of the results
- D. Require that the application development team renews the farm certificate and includes a wildcard for the
'local' domain in the certificate SAN field
Answer: A
NEW QUESTION # 59
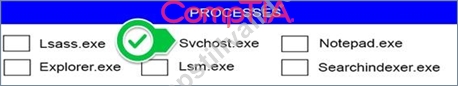
Malware is suspected on a server in the environment. The analyst is provided with the output of commands from servers in the environment and needs to review all output files in order to determine which process running on one of the servers may be malware. Servers 1, 2 and 4 are clickable. Select the Server which hosts the malware, and select the process which hosts this malware.
Instructions:
If any time you would like to bring back the initial state of the simulation, please select the Reset button.
When you have completed the simulation, please select the Done button to submit. Once the simulation is submitted, please select the Next button to continue.
Answer:
Explanation:
Explanation
NEW QUESTION # 60
......
CS0-001 Questions Truly Valid For Your CompTIA Exam: https://www.dumpstillvalid.com/CS0-001-prep4sure-review.html
