


2024 Provide Updated Microsoft MS-102 Dumps as Practice Test and PDF
MS-102 Dumps are Available for Instant Access
Microsoft MS-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
NEW QUESTION # 206
You have a Microsoft 365 tenant that is signed up for Microsoft Store for Business and contains the users shown in the following table.
All users have Windows 10 Enterprise devices.
The Products & services settings in Microsoft Store for Business are shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Text Description automatically generated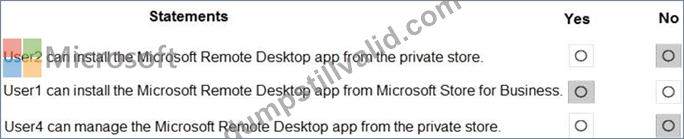
Reference:
https://docs.microsoft.com/en-us/microsoft-store/roles-and-permissions-microsoft-store-for-business
NEW QUESTION # 207
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it as a result these questions will not appear in the review screen.
Your network contains an Active Directory forest.
You deploy Microsoft 365.
You plan to implement directory synchronization.
You need to recommend a security solution for the synchronized identities. The solution must meet the following requirements:
* Users must be able to authenticate successfully to Microsoft 365 services if Active Directory becomes unavailable.
* User passwords must be 10 characters or more.
Solution: implement password hash synchronization and modify the password settings from the Default Domain Policy in Active Directory.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION # 208
HOTSPOT
You have a Microsoft 365 E5 subscription that contains a user named User1.
Azure AD Password Protection is configured as shown in the following exhibit.
User1 attempts to update their password to the following passwords:
F@lcon
Project22
T4il$pin45dg4
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.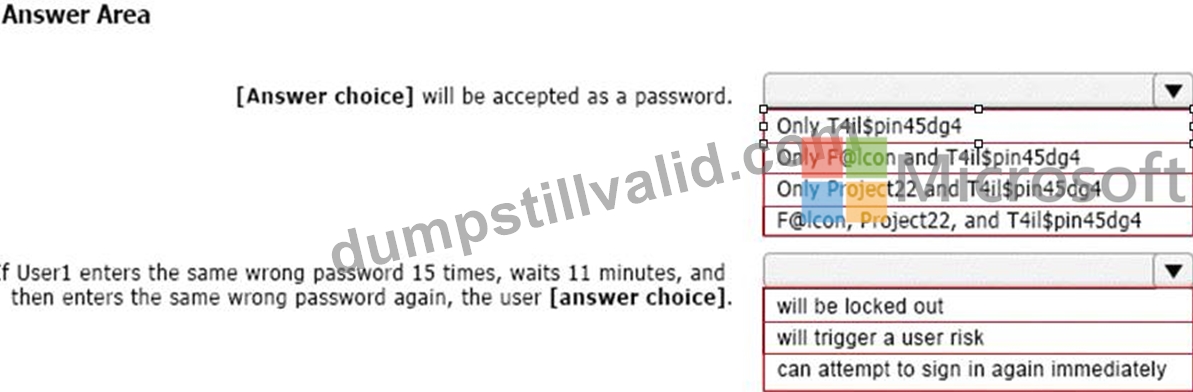
Answer:
Explanation: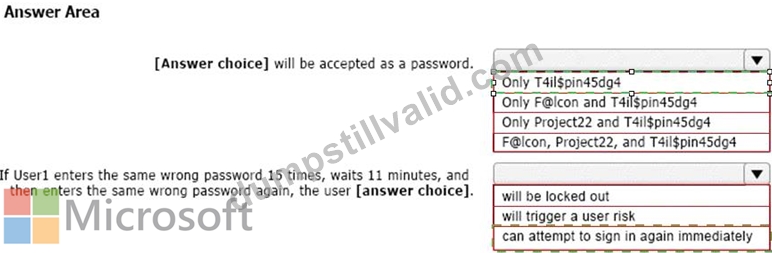
Explanation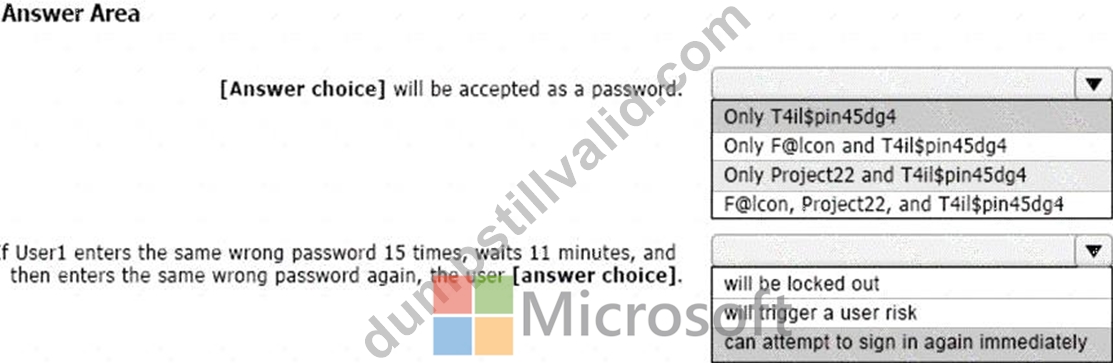
Box 1: Only T4il$pin45dg4
Box 2: can attempt to sign in immediately
Note: Manage Azure AD smart lockout values
Based on your organizational requirements, you can customize the Azure AD smart lockout values.
Customization of the smart lockout settings, with values specific to your organization, requires Azure AD Premium P1 or higher licenses for your users. Customization of the smart lockout settings is not available for Azure China 21Vianet tenants.
To check or modify the smart lockout values for your organization, complete the following steps:
Sign in to the Entra portal.
Search for and select Azure Active Directory, then select Security > Authentication methods > Password protection.
Set the Lockout threshold, based on how many failed sign-ins are allowed on an account before its first lockout.
The default is 10 for Azure Public tenants and 3 for Azure US Government tenants.
Set the Lockout duration in seconds, to the length in seconds of each lockout.
The default is 60 seconds (one minute).
If the first sign-in after a lockout period has expired also fails, the account locks out again. If an account locks repeatedly, the lockout duration increases.
Reference:
https://learn.microsoft.com/en-us/azure/active-directory/authentication/howto-password-smart-lockout
NEW QUESTION # 209
You have a Microsoft 365 E5 tenant that contains five devices enrolled in Microsoft Intune as shown in the following table.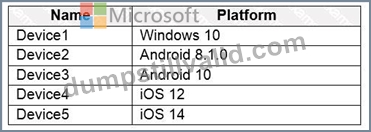
All the devices have an app named App1 installed.
You need to prevent users from copying data from App1 and pasting the data into other apps.
Which policy should you create in Microsoft Endpoint Manager, and what is the minimum number of required policies? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, application, table Description automatically generated
Reference:
https://docs.microsoft.com/en-us/mem/intune/apps/app-protection-policy
NEW QUESTION # 210
You create the planned DLP policies.
You need to configure notifications to meet the technical requirements.
What should you do?
- A. From the Microsoft 365 admin center, configure a Briefing email.
- B. From the Microsoft 365 compliance center, configure the Endpoint DLP settings.
- C. From the Microsoft Endpoint Manager admin center, configure a custom notification.
- D. From the Microsoft 365 security center, configure an alert policy.
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-configure-view-alerts-policies?view=o365-worl
Topic 4, FabrikamOverview
Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment
Active Directory Environment
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication. Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as DNS servers.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements
Planned Changes
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
Project2: After the successful completion of Project1, Microsoft Teams will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft
365 bulk licenses.
Technical Requirements
Fabrikam identifies the following technical requirements:
All users must be able to exchange email messages successfully during Project1 by using their current email address.
Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
A user named User1 must be able to view all DLP reports from the Microsoft Purview compliance portal.
Microsoft 365 Apps for enterprise applications must be installed from a network share only.
Disruptions to email access must be minimized.
Application Requirements
Fabrikam identifies the following application requirements:
An on-premises web application named App1 must allow users to complete their expense reports online.
App1 must be available to users from the My Apps portal.
The installation of feature updates for Microsoft 365 Apps for enterprise must be minimized.
Security Requirements
Fabrikam identifies the following security requirements:
After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
The membership of the UserLicenses group must be validated monthly. Unused user accounts must be removed from the group automatically.
After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
The principle of least privilege must be used.
NEW QUESTION # 211
You are evaluating the required processes for Project1.
You need to recommend which DNS record must be created while adding a domain name for the project.
Which DNS record should you recommend?
- A. text (TXT)
- B. host information
- C. host (A)
- D. pointer (PTR)
Answer: D
Explanation:
Explanation
When you add a custom domain to Office 365, you need to verify that you own the domain. You can do this by adding either an MX record or a TXT record to the DNS for that domain.
Note:
There are several versions of this question in the exam. The question has two possible correct answers:
Text (TXT)
Mail exchanger (MX)
incorrect answer options you may see on the exam include the following:
alias (CNAME)
Host (A)
host (AAA)
Pointer (PTR)
Name Server (NS)
host information (HINFO)
pointer (PTR)
Reference:
https://docs.microsoft.com/en-us/office365/admin/get-help-with-domains/create-dns-records-at-any-dns-hosting-
NEW QUESTION # 212
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You enable self-service password reset (SSPR) for Group1. You configure security questions as the only authentication method for SSPR.
Which users can use SSPR, and which users must answer security questions to reset their password? To answer, select the appropriate options in the answer area.
NOTE; Each correct selection is worth one point.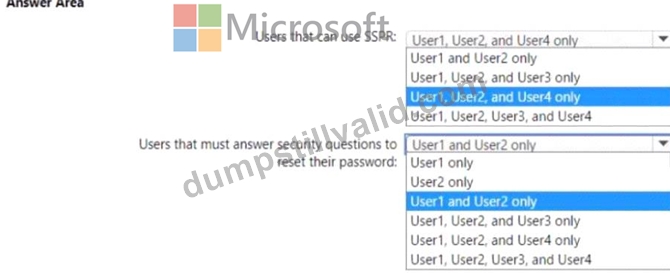
Answer:
Explanation: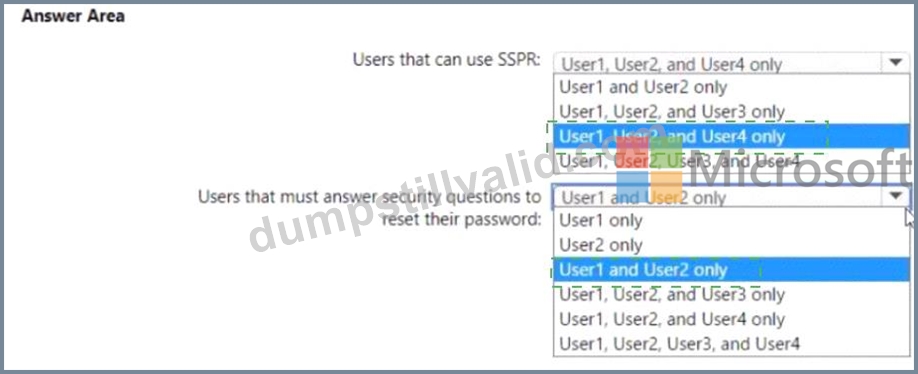
Explanation
NEW QUESTION # 213
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint Online site named Site1.
You need to automatically label the documents on Site1 that contain credit card numbers.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
Graphical user interface, text, application, email Description automatically generated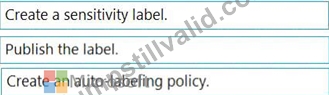
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide#what-labe
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365-wo
NEW QUESTION # 214
You have device compliance policies shown in the following table.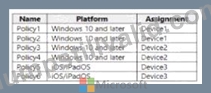
The device compliance state for each policy is shown in the following table.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 215
You have a Microsoft 365 E5 subscription.
On Monday, you create a new user named User1.
On Tuesday, User1 signs in for the first time and perform the following actions:
* Signs in to Microsoft Exchange Online from an anonymous IP address
* Signs in to Microsoft SharePoint Online from a device in New York City.
* Establishes Remote Desktop connections to hosts in Berlin and Hong Kong, and then signs in to SharePoint Online from the Remote Desktop connections Which types of sign-in risks will Azure AD Identity Protection detect for User1?
- A. anonymous IP address and atypical travel
- B. anonymous IP address, atypical travel, and unfamiliar sign-in properties
- C. anonymous IP address only
- D. anonymous IP address and unfamiliar sign-in properties only
- E. unfamiliar sign-in properties and atypical travel only
Answer: C
NEW QUESTION # 216
You have a Microsoft 365 E5 tenant that contains the users shown in the following table.
You provision the private store in Microsoft Store for Business.
You assign Microsoft Store for Business roles to the users as shown in the following table.
You need to identify which users can add apps to the private store, and which users can assign apps from Microsoft Store for Business.
Which users should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Graphical user interface, text, application Description automatically generated
Reference:
https://docs.microsoft.com/en-us/microsoft-store/roles-and-permissions-microsoft-store-for-business
https://docs.microsoft.com/en-us/education/windows/education-scenarios-store-for-business#basic-purchaser-rol
NEW QUESTION # 217
You have a Microsoft 365 E5 tenant that contains four devices enrolled in Microsoft Intune as shown in the following table.
You plan to deploy Microsoft 365 Apps for enterprise by using Microsoft Endpoint Manager.
To which devices can you deploy Microsoft 365 Apps for enterprise?
- A. Device1 and Device3 only
- B. Device1 only
- C. Device1, Device2. and Device3 only
- D. Device1, Device2, Device3, and Device4
- E. Device2 and Device4 only
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/mem/intune/apps/apps-add
NEW QUESTION # 218
You have a Microsoft 365 subscription.
Your company has a customer ID associated to each customer. The customer IDs contain 10 numbers followed by 10 characters. The following is a sample customer ID: 12-456-7890-abc-de-fghij.
You plan to create a data loss prevention (DLP) policy that will detect messages containing customer IDs.
D18912E1457D5D1DDCBD40AB3BF70D5D
What should you create to ensure that the DLP policy can detect the customer IDs?
- A. a supervision policy
- B. a sensitive information type
- C. a retention label
- D. a sensitivity label
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/custom-sensitive-info-types?view=o365-worldwide
NEW QUESTION # 219
You have a Microsoft 365 E5 subscription.
You need to create a mail-enabled contact.
Which portal should you use?
- A. the Microsoft 365 admin center
- B. the SharePoint admin center
- C. the Microsoft Purview compliance portal
- D. the Microsoft Entra admin center
Answer: A
NEW QUESTION # 220
Your on-premises network contains an Active Directory domain.
You have a Microsoft 365 E5 subscription.
You plan to implement a hybrid configuration that has the following requirements:
* Minimizes the number of times users are prompted for credentials when they access Microsoft 365 resources
* Supports the use of Azure AD Identity Protection
You need to configure Azure AD Connect to support the planned implementation. Which two options should you select? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Pass-through authentication
- B. Directory extension attribute sync
- C. Password writeback
- D. Password Hash Synchronization
- E. Enable single sign-on
Answer: C,D
NEW QUESTION # 221
You have a Microsoft 365 subscription.
You create a retention label named Retention1 as shown in the following exhibit.
You apply Retention! to all the Microsoft OneDrive content.
On January 1, 2020, a user stores a file named File1 in OneDrive.
On January 10, 2020, the user modifies File1.
On February 1, 2020, the user deletes File1.
When will File1 be removed permanently and unrecoverable from OneDrive?
- A. February 1, 2020
- B. July 1.2020
- C. August 1, 2020
- D. July 10, 2020
Answer: B
NEW QUESTION # 222
HOTSPOT
You have a Microsoft 365 E5 subscription.
From Azure AD Privileged Identity Management (PIM), you configure Role settings for the Global Administrator role as shown in the following exhibit.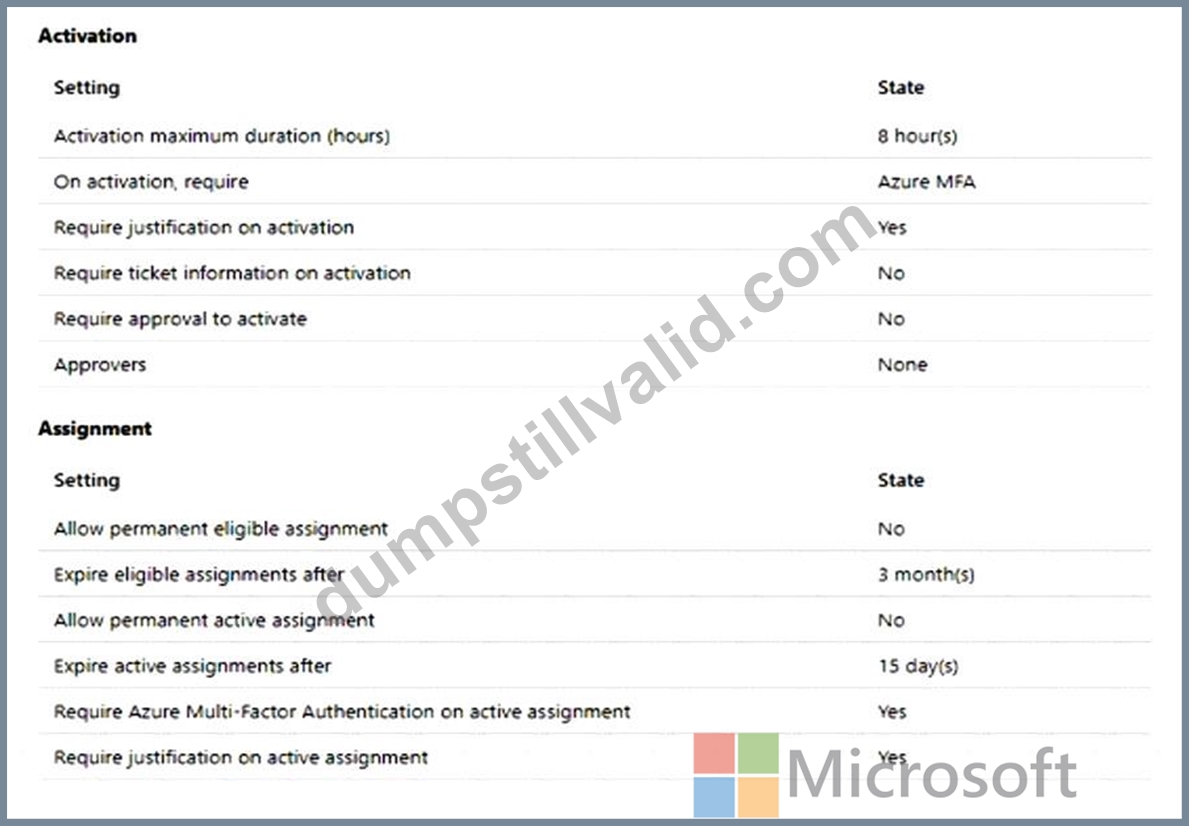
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.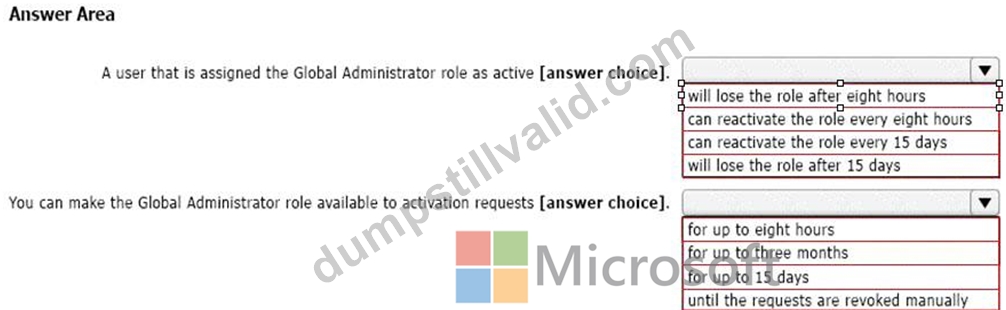
Answer:
Explanation:
Explanation
Box 1: will lose the role after eight hours
From exhibit: Activation, Activation maximum duration (hours): 8 hour(s) Box 2: for up to three months We see from exhibit: Assignment, Expire eligible assignment after: 3 month(s)
NEW QUESTION # 223
HOTSPOT
Your company uses Microsoft Defender for Endpoint. Microsoft Defender for Endpoint includes the device groups shown in the following table.
You onboard a computer named computer1 to Microsoft Defender for Endpoint as shown in the following exhibit.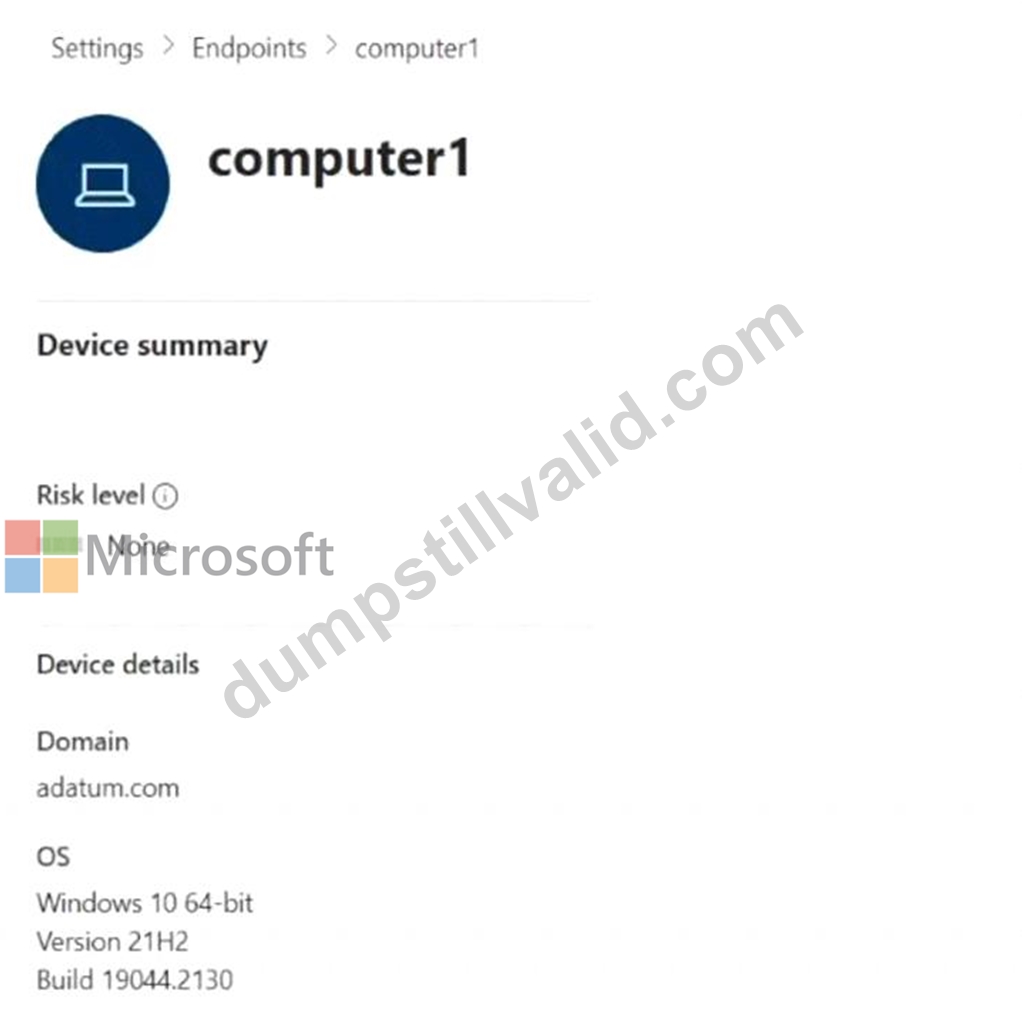
Use the drop-down menus to select the answer choice that completes each statement.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Box 1: Group3 and Group4 only
Computer1 has no Demo Tag.
Computer1 is in the adatum domain and OS is Windows 10.
Box 2: Group1, Group2, Group3 and Group4
NEW QUESTION # 224
......
Updated MS-102 Dumps Questions For Microsoft Exam: https://www.dumpstillvalid.com/MS-102-prep4sure-review.html
Valid MS-102 Dumps for Helping Passing MS-102 Exam!: https://drive.google.com/open?id=11qF1TsO6pVqmd6ITft1f9aPnaRrjChwF
